
Kauai Hemp Co
How we repeatedly cleaned a compromised WooCommerce store, hardened it against recurring attacks, audited and disavowed toxic backlinks, and resolved persistent SEMrush technical issues to keep kauaihempco.com clean, secure, and fully indexed.
Visit WebsiteChallenges Faced
Kauai Hemp Co's WooCommerce store was hit by repeated malware compromises that survived a prior hosting-level cleanup, carried a long list of outdated and vulnerable plugins, and was sitting on an unaudited backlink profile and unresolved technical SEO issues.
Recurring Malware That Kept Coming Back
Malicious files regenerated even after the hosting provider ran its own cleanup, redirecting Googlebot to third-party domains. A hidden backdoor file (xml.php) allowed admin login without credentials — the root cause the hosting-level fix had missed.
Site Hijack: GSC Access & Discount Code Abuse
An attacker planted a Search Console verification tag to gain unauthorized owner-level access, created rogue WooCommerce discount codes, and littered the site with spam links and 404 pages during a full site compromise.
A Long Tail of Vulnerable, Abandoned Plugins
The site was carrying outdated and vulnerable plugins — including a 13-plugin Soliloquy suite, Slider Revolution and its add-ons, and Forminator — plus plugins removed entirely from the WordPress.org repository, widening the attack surface.
Persistent Technical SEO & Backlink Risk
A stubborn XML sitemap whitespace bug kept resurfacing in Semrush, schema and merchant-listing validation was failing, and the backlink profile had never been systematically audited for toxic domains.
Our Strategy
A security-first approach — remove the malware at its root, lock down access, cut the plugin attack surface, then clean up technical SEO and backlink risk.
-
Identified and permanently removed hidden malicious files that had survived a prior hosting-level cleanup and kept regenerating malware
-
Found and deleted a backdoor file (xml.php) that allowed automatic admin login without credentials
-
Updated WordPress core, themes, and active plugins to their latest secure versions, and cleaned modified core files flagged by security scans
-
Ran repeated follow-up scans over multiple weeks to confirm no new malicious files were being regenerated
-
Investigated and removed an unauthorized Search Console verification tag that had granted an outside party owner-level GSC access
-
Changed the default WordPress login URL, reset compromised admin passwords, and recommended 2FA on every admin account
-
Cleaned up unauthorized WooCommerce discount codes and removed the spam links and 404 pages left behind after the site was compromised
-
Recommended Wordfence Premium for real-time firewall protection, brute-force prevention, and country blocking
-
Deactivated and removed 20+ vulnerable, unused, or abandoned plugins, including the 13-plugin Soliloquy suite, Slider Revolution and its add-ons, and Judge.me Product Reviews
-
Flagged plugins removed entirely from the WordPress.org repository — Creative Mail and USPS (Basic) WooCommerce Shipping — for client-approved replacement
-
Kept Forminator under active monitoring for an official vendor patch while its vulnerability remained unresolved upstream
-
Reviewed all administrator accounts and flagged the two client-owned Super Administrator accounts for immediate password resets and 2FA
-
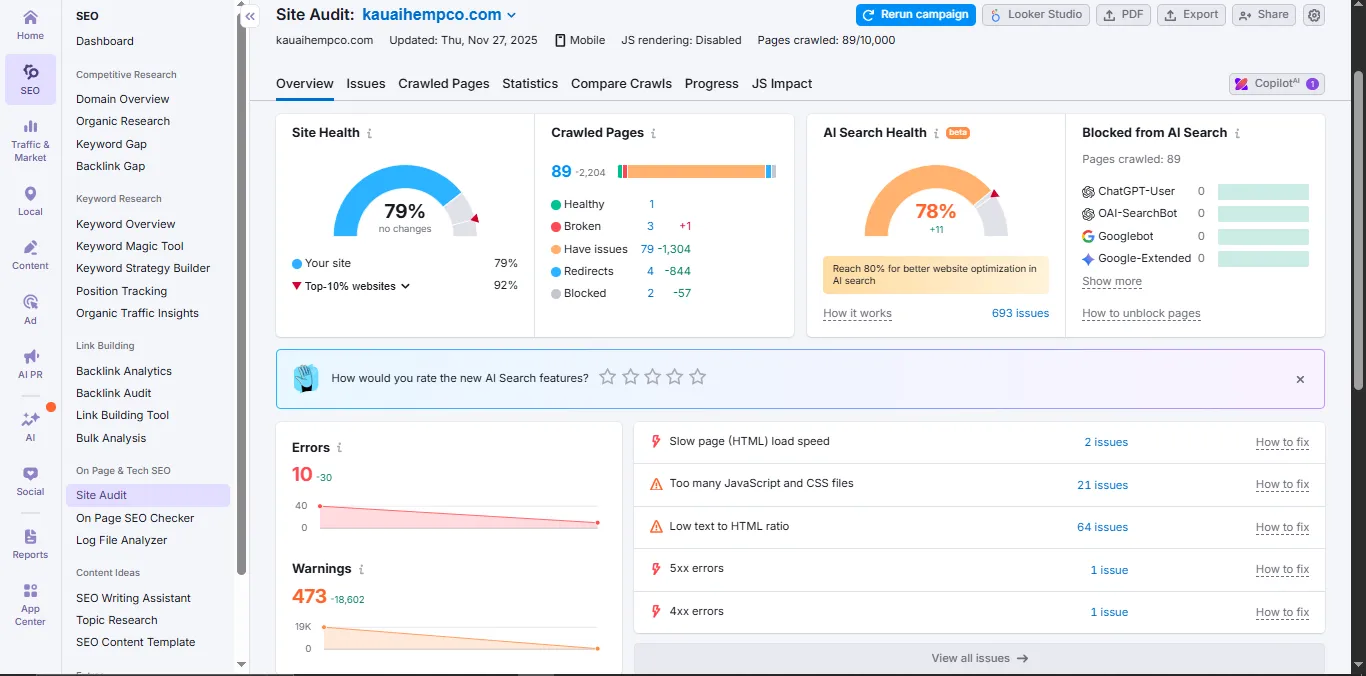
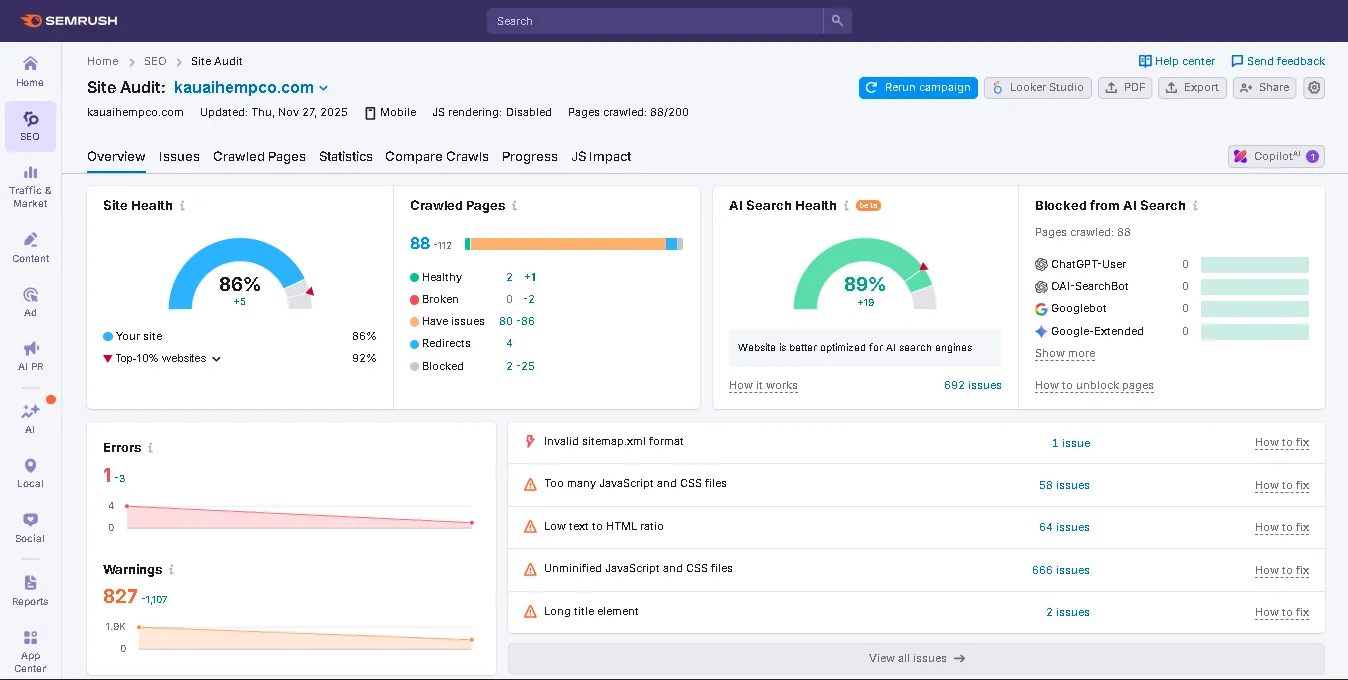
Resolved recurring SEMrush technical issues and traced a persistent XML sitemap whitespace bug down to the server level
-
Fixed schema and merchant-listing validation errors flagged in Google Search Console and resubmitted the XML sitemap
-
Ran a full SEMrush backlink audit combining manual and AI-based review, then disavowed toxic domains through the GSC Disavow Tool
-
Brought sitemap URL indexing in Google Search Console up to 100%, requesting indexing for every remaining URL
Results That Speak
Measurable improvements across site security, plugin risk, indexing, and technical SEO health.
Active Malware Detections
Vulnerable Plugins Resolved
Sitemap URLs Indexed
Semrush Site Health Score
Before & After
Semrush technical audit results before and after remediation.
Kauai Hemp Co
Kauai Hemp Co is a hemp and CBD e-commerce brand selling through a WooCommerce-powered WordPress store. After being targeted by repeated malware and access-hijacking attempts, the company needed a security partner who could remove the root cause of each attack, harden the site against future compromise, and keep its technical SEO and backlink profile healthy.
Kauai Hemp Co
Hemp & CBD E-Commerce — WooCommerce
Small Issues, Big Losses —
We Solve Both
A hacked or vulnerable WordPress site puts your customers, your rankings, and your revenue at risk. Let our security and technical SEO specialists find the root cause, lock it down, and keep it that way.